HIPAA compliance software for small healthcare practices
Do your yearly HIPAA risk assessment, adopt written policies, train your staff and track your BAAs, all in one place. Built for small practices and the vendors that serve them. Every plan includes unlimited users.
14 days free. No card needed to start. Plans from $120 a month.

Who it's for
Medical, dental and therapy practices
Your yearly risk assessment, written policies and staff training records in one place.
About the risk assessmentVendors that handle patient data (business associates)
Answer customer security reviews with your risk assessment, policies and evidence.
Tools for vendorsIT providers and consultants
Refer your healthcare clients today. A white-label partner program is planned.
For IT providersWhat you get
Screens from Polestar GRC, shown with demo data.
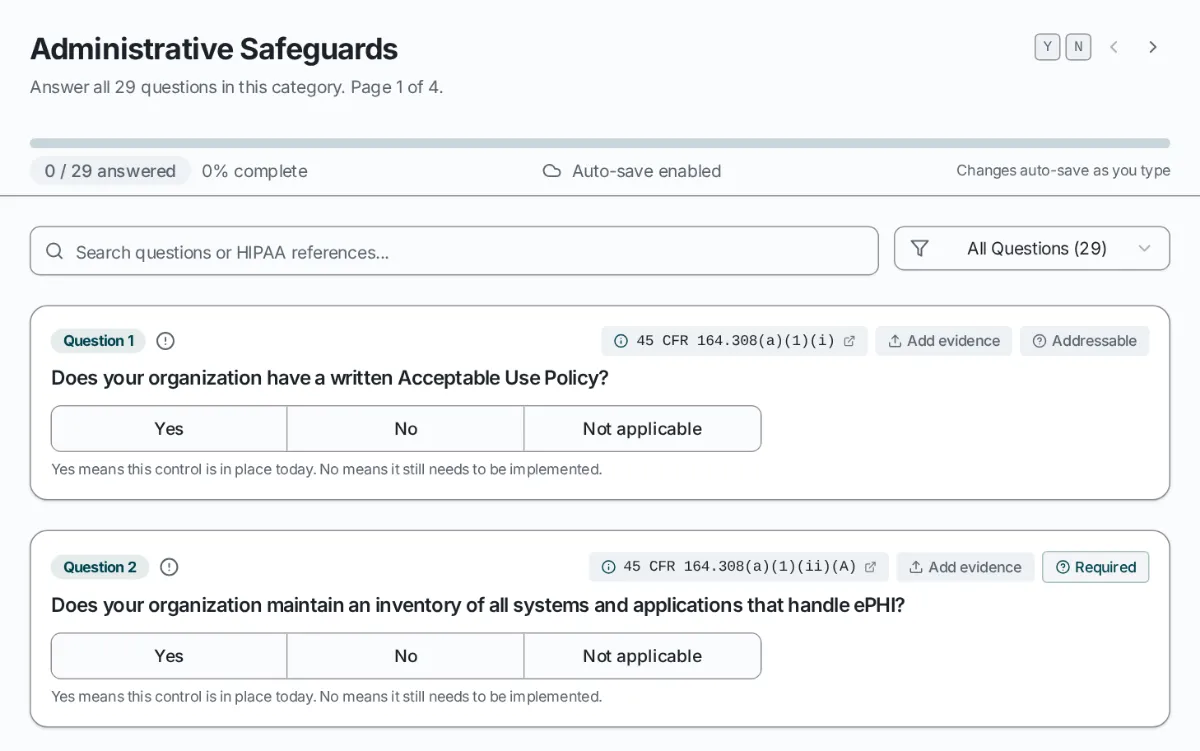
Risk assessment report
Plain yes or no questions, each citing the HIPAA rule it covers. A PDF report and a fix list at the end.

Written policies
Templates for every HIPAA required standard, customized to your practice and your state.

Staff training records
A 5-minute lesson by email each month, and a record of who finished it.

Vendor and BAA tracker
Track every vendor that handles your patient data, and when each agreement expires.

Breach deadline clock
Log an incident and see your notice deadlines. Breach deadlines for all 50 states and DC, plus state documents where a statute requires one. Check your state's breach deadline.
How it works
Answer plain questions
The assessment skips what does not apply to you. Your answers save as you go.
Fix the gaps
Every "no" lands on your task list. Adopt policies, train staff and add vendors as you go.
Share your records
When an auditor or a customer asks, download your report, policies and evidence.
Why you can trust it
- Every question cites the HIPAA rule it covers, so you can trace each finding back to the rule.
- We do not certify anyone as HIPAA compliant, and no one can. We give you the documents and the plan; your practice does the work.
- You can accept our Business Associate Agreement in the app before you add patient information. It is the same agreement on every plan, including the free trial.
- Your data is encrypted in transit and at rest. Read how we protect it.
- Built and run by Jonathan Prine. About Polestar GRC.
Questions
- Do you sign a BAA?
- Yes. You can accept our Business Associate Agreement in the app before you add patient information. It is the same agreement on every plan, including the free trial. An administrator accepts it from the BAA Tracker: a Business Associate Agreement for covered entities, a Subcontractor BAA for business associates, and a Data Protection Agreement for organizations outside HIPAA. Until it is accepted, new uploads and incident details wait.
- How long does it take?
- It depends on the size of your practice and how much paperwork you already have. You do not have to finish in one sitting: answers save as you go, and your dashboard shows the next step.
- What if we already did an assessment?
- Import the yes, no and not applicable answers from your earlier assessment as a CSV file, then work on the gaps from your task list and keep the assessment current here.
- How is data protected?
- Data is encrypted in transit (TLS 1.2 or higher) and at rest (AES-256 on our database volumes, file storage and backups). Every request is checked against your organization, and roles control what each member can do inside your workspace. Multi-factor authentication can be required for your whole workspace, and security-relevant actions, such as role and MFA changes and blocked access attempts, are recorded in an audit log. Read more on our Security page.
- Prefer video? Watch our step-by-step guides
- Short narrated videos walk through each step in the app, from setup and the risk assessment to policies, BAAs and audit readiness. There is a series for practices, one for vendors and one for nonprofits outside HIPAA, each with captions. Watch the video guides.
Start your HIPAA program today
Begin with the risk assessment. Your dashboard shows the next step.
14 days free. No card needed to start.