HIPAA risk assessment
HIPAA risk assessment for small practices
Do your yearly HIPAA Security Risk Assessment online. The questions fit your practice, each one cites the rule, and you finish with a PDF report and a list of what to fix.
14 days free. No card needed to start. Included in every plan, from $120 a month.
What is a HIPAA risk assessment?
The HIPAA Security Rule requires every covered entity and business associate to do "an accurate and thorough assessment" of the risks to the electronic patient information it holds (45 CFR 164.308(a)(1)(ii)(A)). HHS calls this a risk analysis. Most people call it a security risk assessment, or SRA.
In plain words: list where patient information lives, find what could go wrong, rate how likely and how bad each risk is, and write down what you will do about it. Then keep it current. The rule sets no schedule, but most practices review it every year and after a big change, such as a new records system or a move.
If you report under MIPS Promoting Interoperability, you also attest each year that you did or reviewed a security risk analysis. Polestar GRC helps you do and document the analysis; it does not file anything with CMS.
What our assessment covers
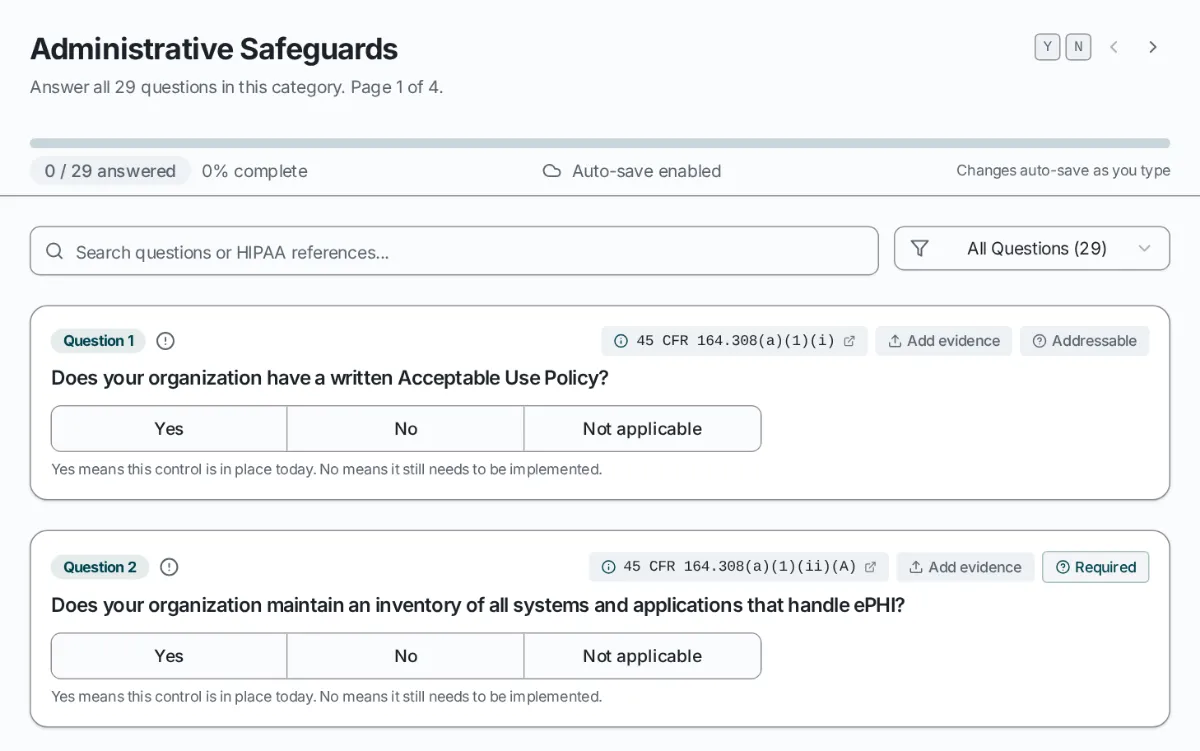
Questions come from a 174-question library. You only see the ones that apply to your type of organization and your HIPAA role, and every question names the rule it covers.
- Administrative safeguards (45 CFR 164.308): risk management, workforce training, access management, contingency planning
- Physical safeguards (45 CFR 164.310): facility access, workstations, devices and media
- Technical safeguards (45 CFR 164.312): access control, audit controls, integrity, transmission security
- Privacy Rule and Breach Notification Rule questions where they apply to you
- Questions on the Security Rule changes HHS proposed on January 6, 2025, marked as proposals, not final requirements
What you get at the end
- A PDF report of your answers, gaps and remediation plan, organized by safeguard.
- A risk register and task list. Every "no" becomes a gap you track until it is fixed.
- A head start. Import yes, no and not applicable answers from an earlier assessment as a CSV file, and attach evidence to any question.
What it does not do
- It does not certify you. No one can certify a practice as HIPAA compliant.
- It is not legal advice, and Polestar GRC is not affiliated with HHS or the Office for Civil Rights.
- HHS also offers a free SRA Tool you can download. Polestar GRC adds the policies, training, vendor tracking and breach workflow that follow from your answers, in one place.
See everything else in the app on the features page.
Start your risk assessment today
Your answers save as you go, so you can stop and come back.
14 days free. No card needed to start.